
For Enterprises
Playbooks, decision frameworks, and case studies written for enterprises.
What a Warranty Period Actually Obligates Your Vendor to Fix
Most UAE enterprise software warranty clauses define a 'defect' against the UAT acceptance document, not production behaviour — which means performance degradation, integration failures, and CBUAE-driven changes are billable from day one. Here is what to change in the MSA before you sign.
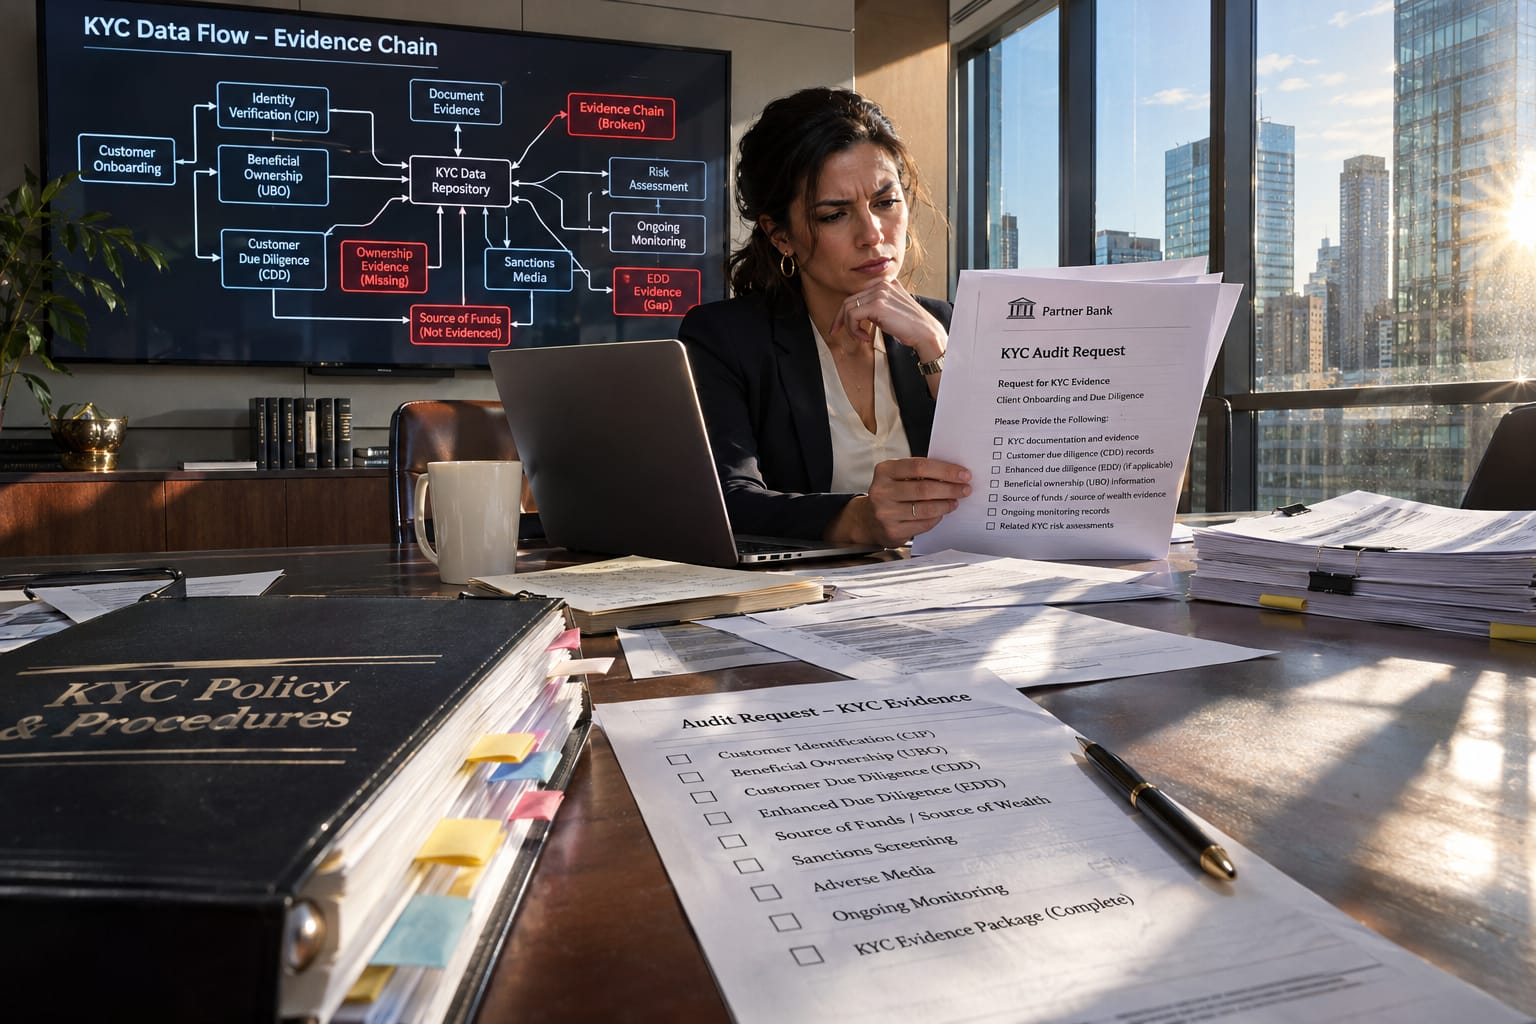
What KYC Actually Requires of Your Software Architecture
Plugging in Persona or Jumio does not make your KYC program auditable. The CIP rule demands a durable, queryable decision record your own database owns — and most vendor widgets never write it there.
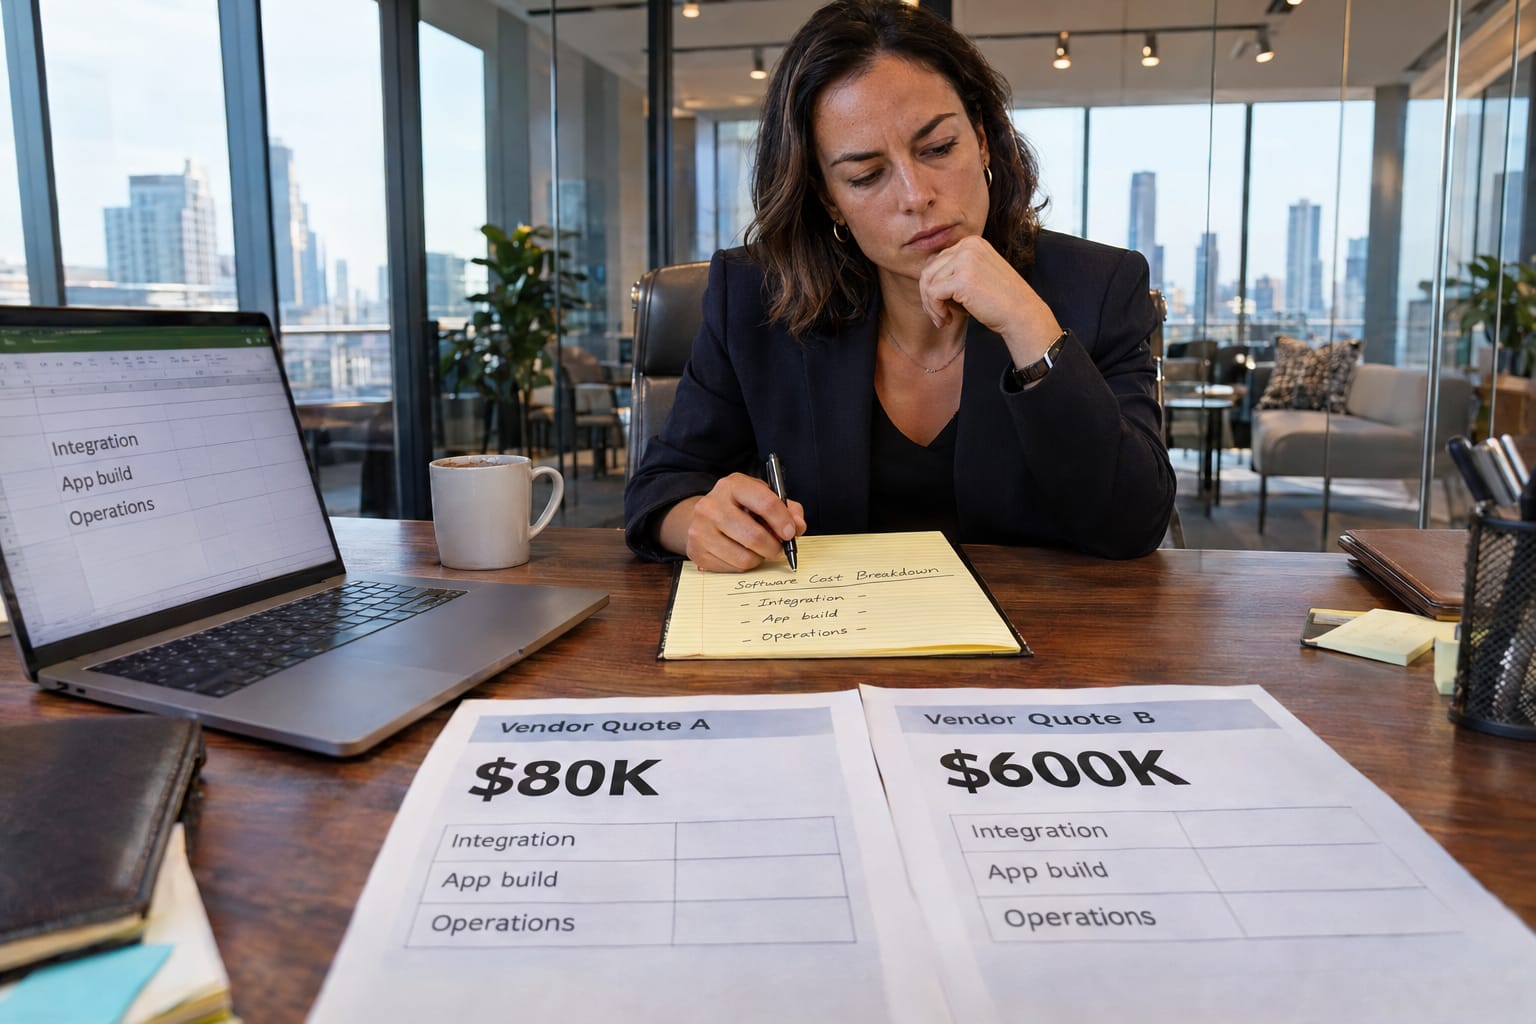
Pricing a Customer Mobile App Before You Brief Anyone
Two vendors just quoted you $80K and $600K for what looks like the same customer mobile app. Here is how to decode the spread, find the cost driver both vendors are hiding, and walk into the CFO's office with a defensible number.
How to Run a Vendor Pilot That Actually Proves Something
Most paid pilots end with the buyer no better equipped to defend the build decision than when they started. Here is a six-step process that forces a vendor to prove capability against your data, your integrations, and your exceptions.
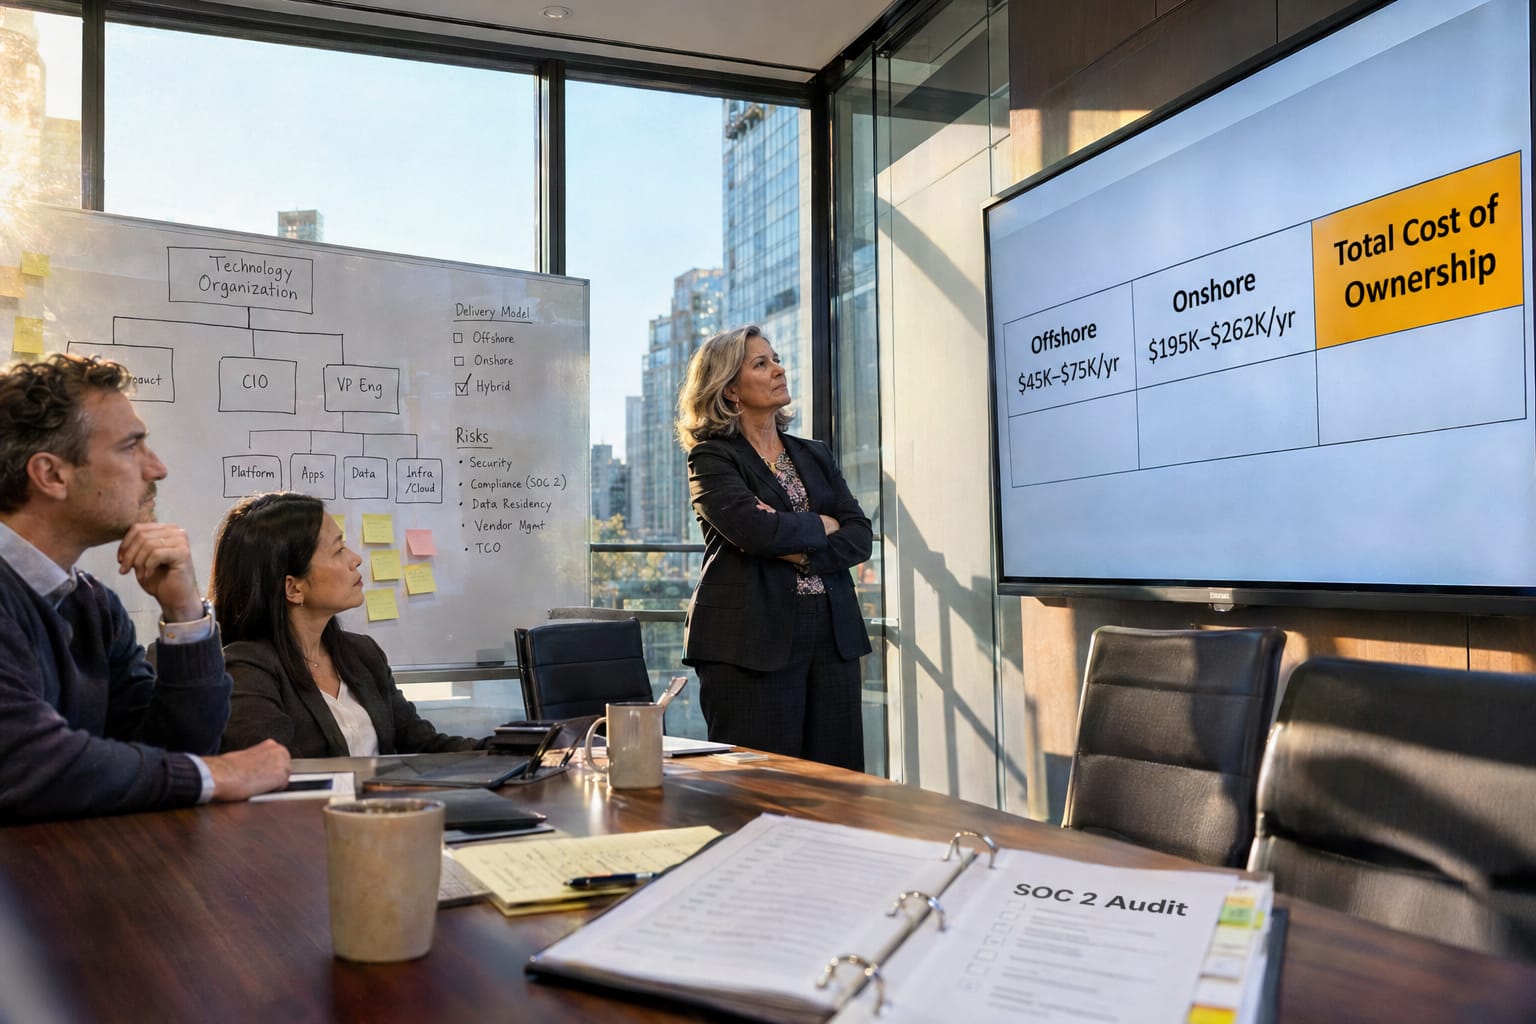
Offshore vs. Onshore Dev: The Decision US Enterprises Get Wrong
The 40–60% rate gap between offshore and onshore developers looks decisive on a spreadsheet and misleading in practice. Here's the decision framework a VP of Engineering actually needs — hidden coordination costs, compliance surcharges, and when each model wins.
What 'We'll Use an AI Agent' Actually Commits You To
When a vendor proposes 'AI agents' to automate an ops workflow, the phrase can mean anything from a chatbot wrapper to a system requiring board-approved governance. Here is how to tell which one you have been quoted, and what you are signing up to maintain for the next three years.
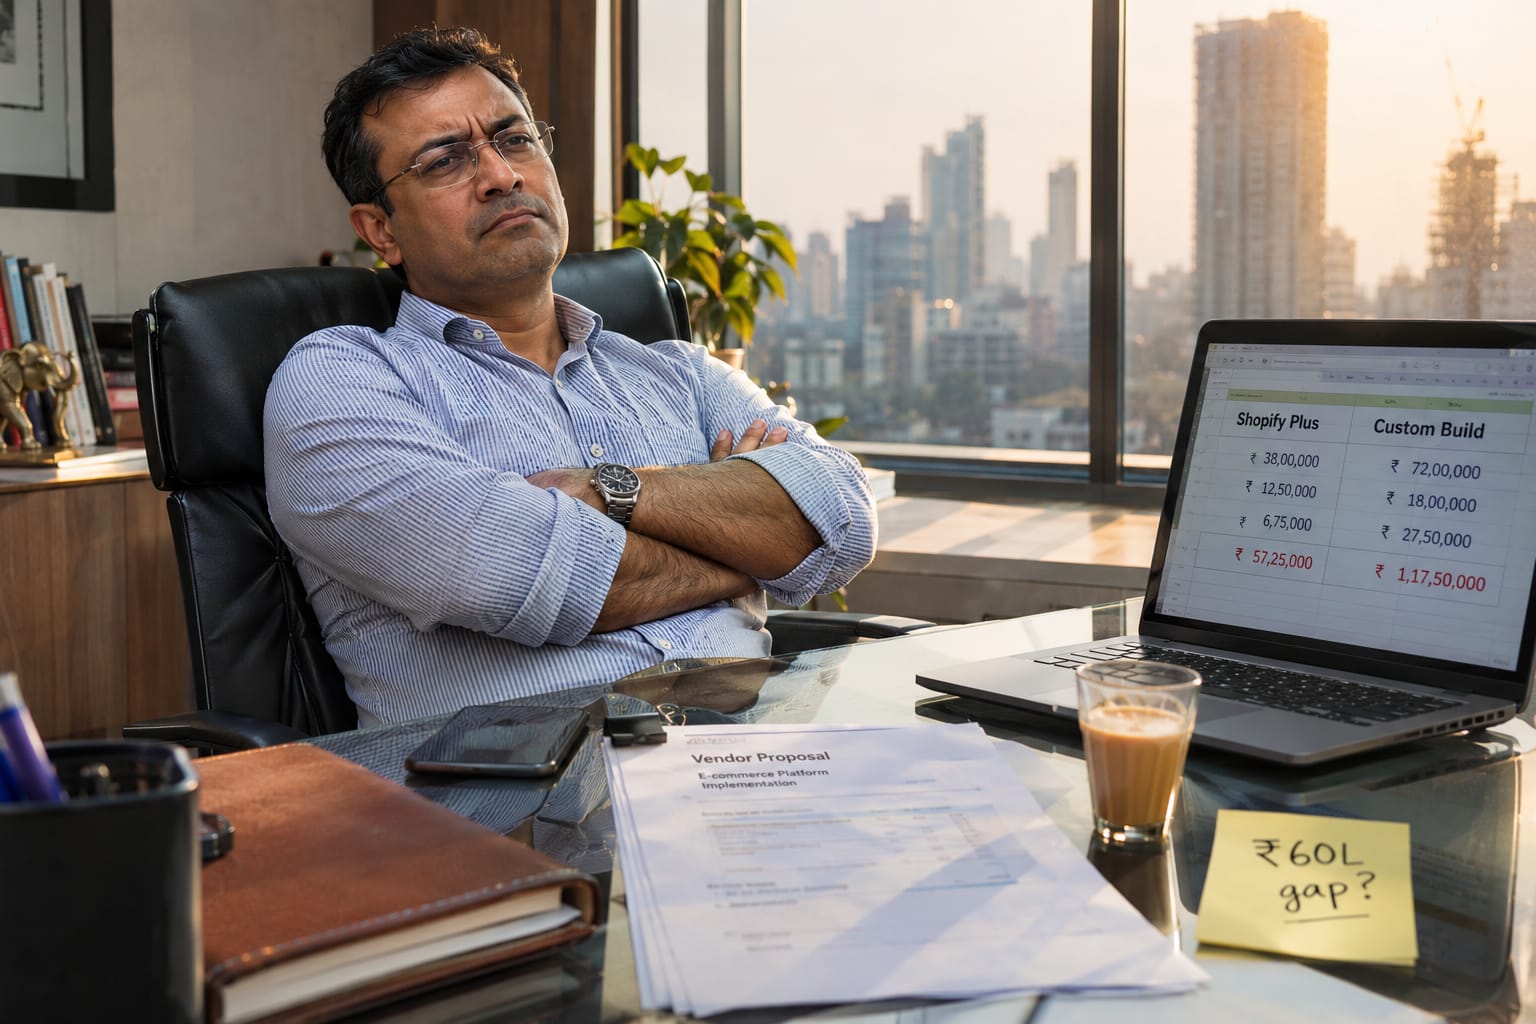
Custom E-Commerce vs. Shopify: Where the Budget Actually Goes
The 10x price gap between a Shopify Plus quote and a custom-build estimate rarely reflects what your CFO thinks it does. Here is where the money actually sits — and the one integration that quietly flips the maths.
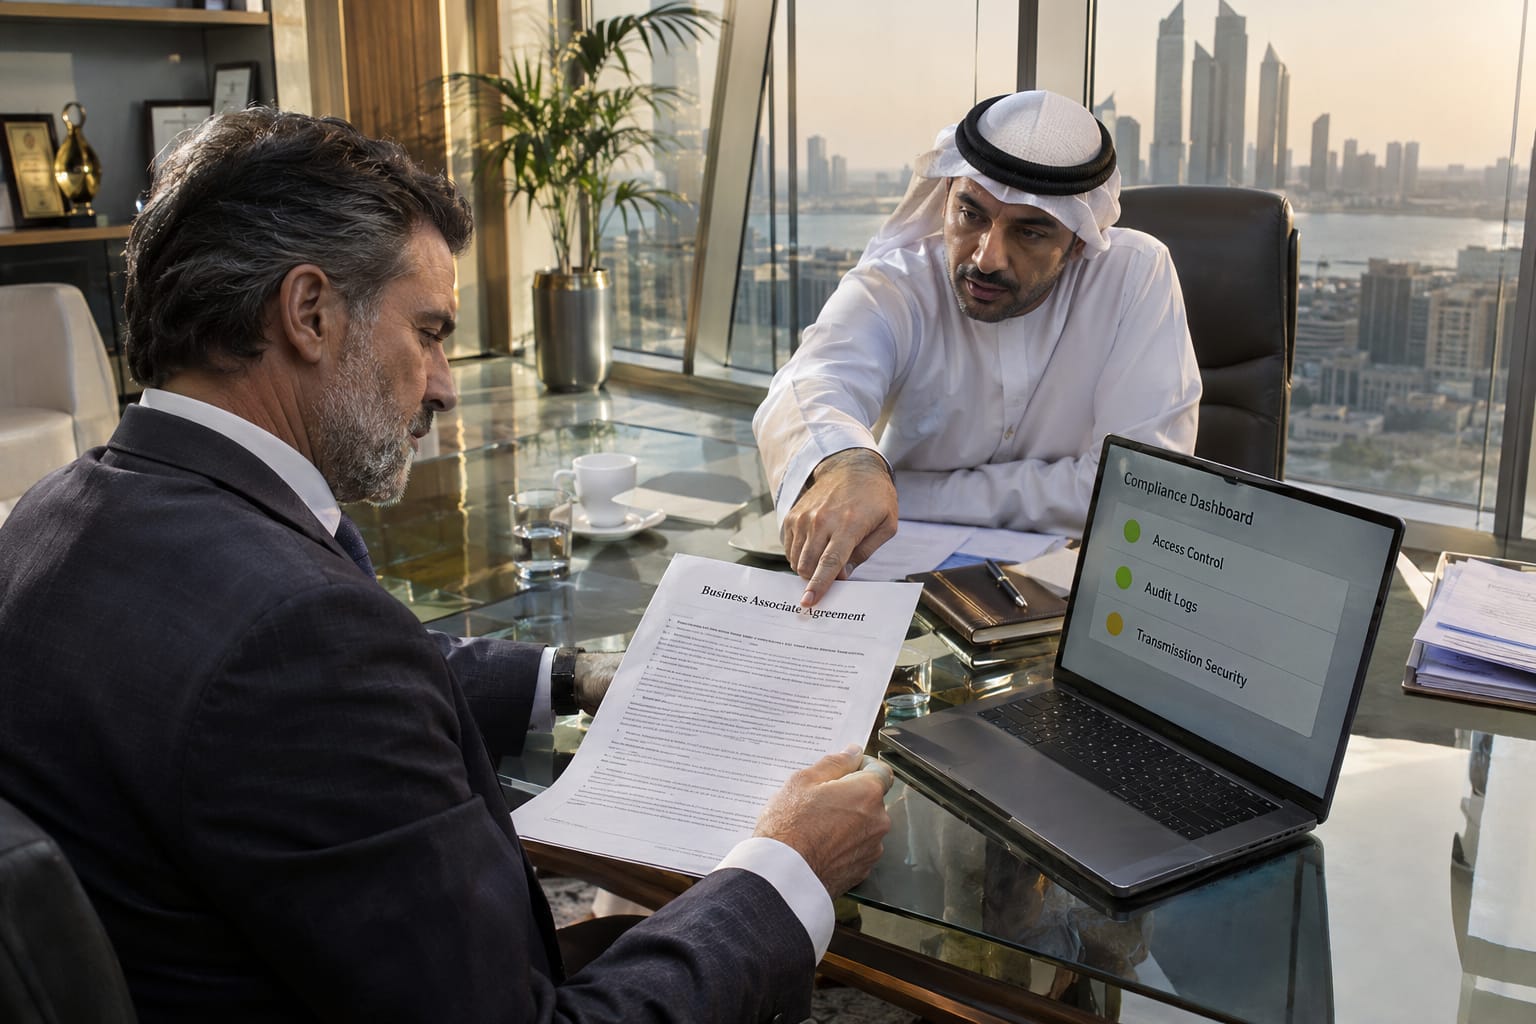
What HIPAA Demands of a UAE Health Tech Vendor You Hire
A signed Business Associate Agreement is legally required but architecturally meaningless on its own. Here is what HIPAA's Security Rule actually demands of a UAE vendor's code, logs, and contracts — and how to tell real compliance from a PDF.
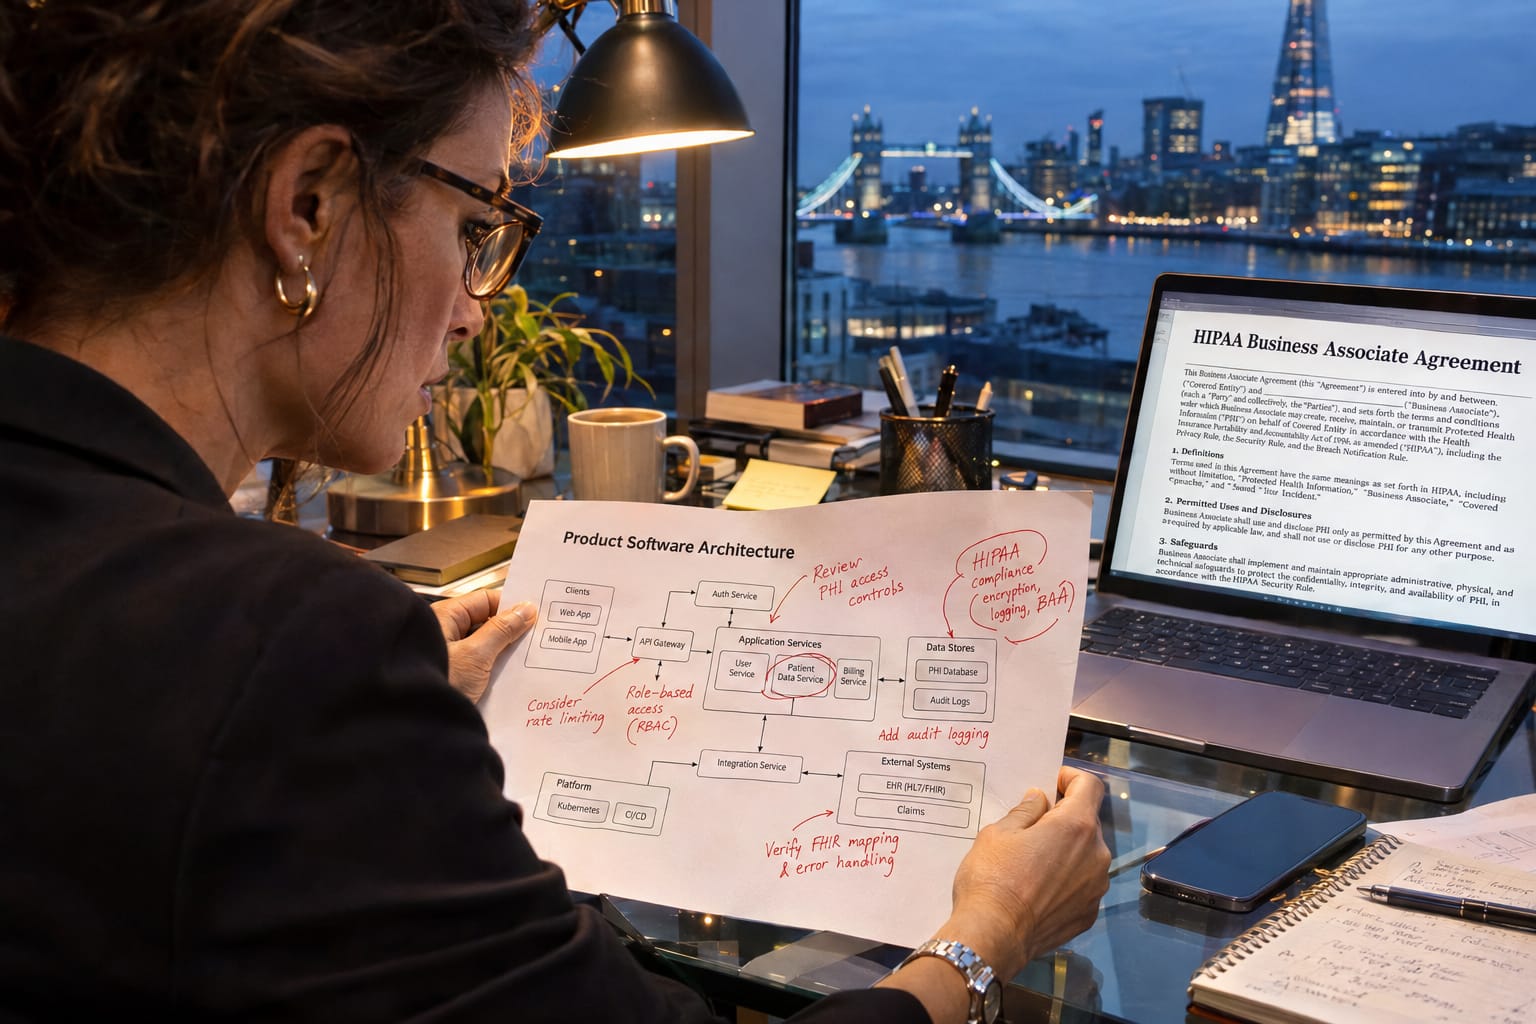
What HIPAA Actually Demands of Your Software Architecture
HIPAA is not a policy binder. The Security Rule demands specific, evidence-producing controls in the running system — and the most common audit failure is an access log that cannot name who touched a patient record and when.
Legacy Migration Without Downtime: The Real Timeline
Most zero-downtime migration quotes ignore the one phase that actually slips: the parallel run. Here is the real elapsed-time breakdown for a 300-person enterprise, phase by phase, with the client-side dependencies that extend each one.
Taking Over a Codebase From a Previous Vendor
Terminating a development vendor is the easy part. The hard part is discovering, three weeks in, that your Stripe account is still under their name and your SOC 2 auditor wants to know why. Here's the playbook a COO or VP Engineering should run.
How US Enterprises Are Billed for AI Dev Work — and Where the Model Breaks
Three AI development proposals, three pricing structures, no way to compare them like-for-like. Here is a buyer's framework for how Big Four consultancies, nearshore body shops, and AI-first studios actually bill — and where each model quietly transfers risk back to you.